Fintech
Onboarding, payments, and ledgers for teams that already have a compliance owner.
Regulated & High-Growth
The vertical
Payment firms, lenders, and product teams that move money or hold balances and cannot treat the ledger as a side table.
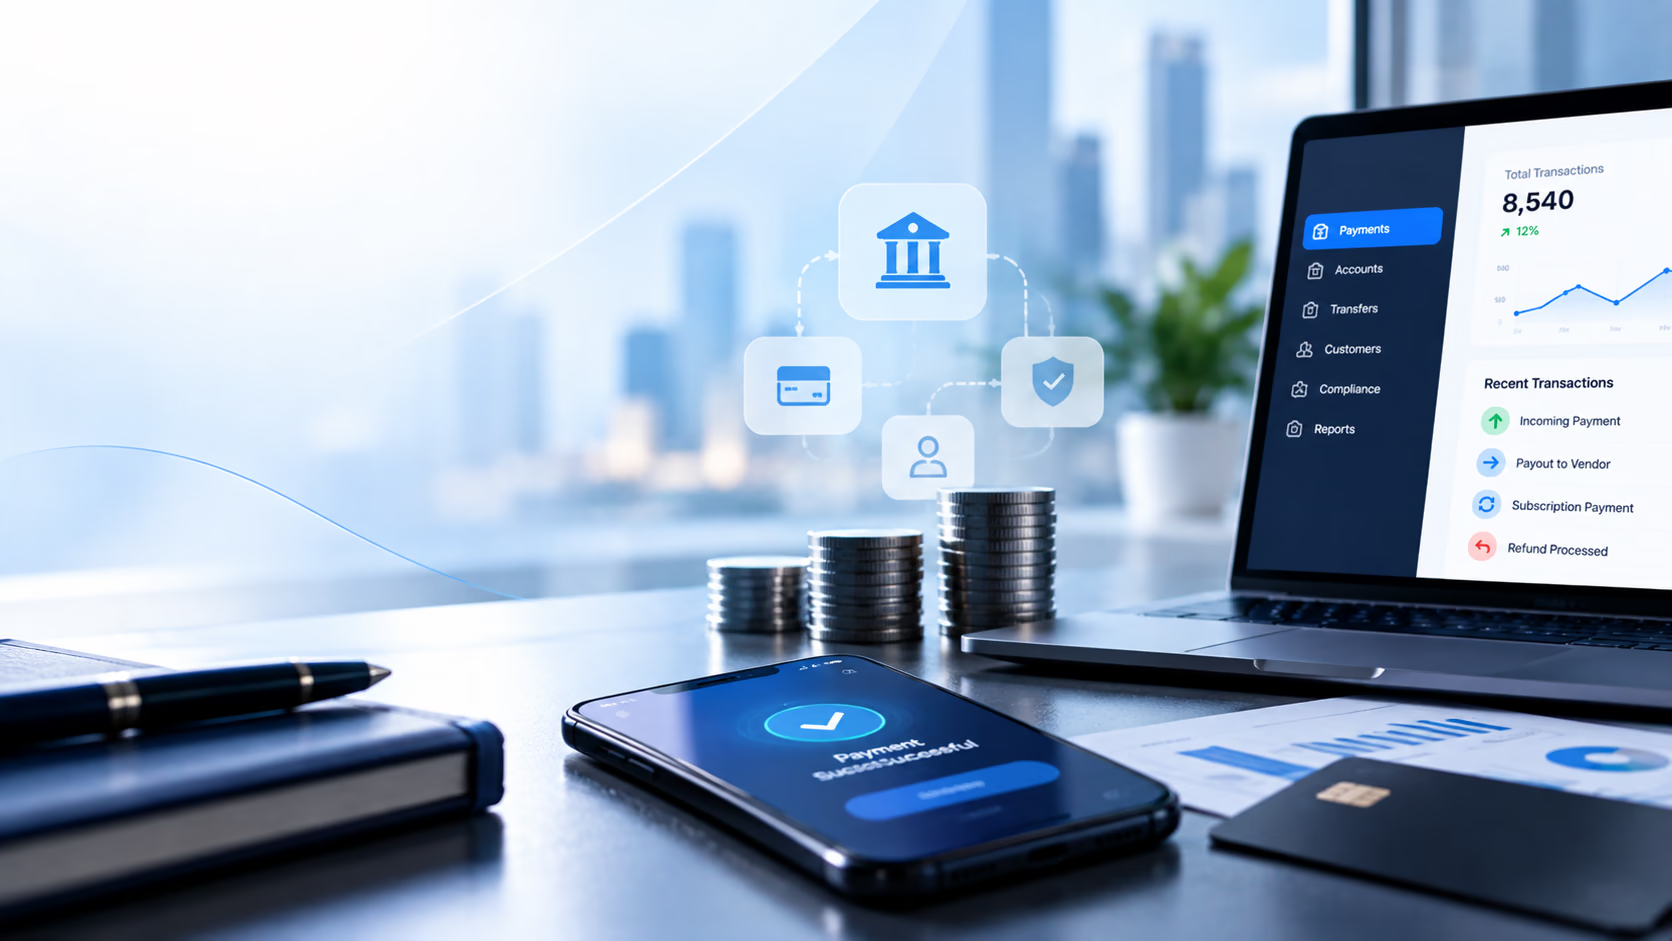
Fintech software at XiteHub is about a ledger you can explain. An applicant becomes a customer with a clear state. A payment posts once, with a retry path that ops can see. Refunds and chargebacks are first-class, not a Slack thread. If you run lending, the schedule and the collection queue share the same account. If you run payouts, the approval sits on the record. We have shipped products that move money and identity for teams across more than 10 countries. The stack is usually boring on purpose: a database you own, queues that retry, and an admin your ops lead will actually open.
Book a walkthroughThe gap
What is usually broken
Onboarding is a folder of PDFs. The ledger is a sheet plus a processor dashboard. Ops cannot say who approved a payout, and engineering cannot replay a failed settlement without a war room.
Approach
How we enter
XiteHub builds the objects finance and ops already argue about: applicants, accounts, payments, and the journal that explains them. We sit beside the processor, the bank file, and the KYC vendor you already use. We do not claim PCI or SOC 2 as a stamp we hold. Your compliance owner names the controls. We implement them in the product: roles, logs, and the reports they file. We will say so if a licensed core or a bureau should stay the source of truth.
Challenges
What we keep hearing
- 01
KYC and onboarding still live in email and a shared drive
- 02
The processor dashboard and the internal ledger do not match at day-end
- 03
Payouts need two signers, but the tool only has one admin
- 04
A core bank or card scheme cannot be replaced, only talked to
- 05
Fraud review is a gut feel because there is no case file
- 06
Engineering cannot replay a failed batch without taking production down
What we build
Work that belongs in this sector
- 01
Applicant and customer files with the checks your compliance owner named
- 02
Payment, refund, and payout flows with an approval trail
- 03
A ledger and day-end pack finance can reconcile to the processor
- 04
Admin queues for exceptions, not a private database console
- 05
Connectors into the bank, card, or KYC vendors you already run
- 06
Read-only audit views for the people who file the reports
Entry
How we start here
Floor first, then the systems that stay, then a slice operators will use. We do not lead with a generic industry pack.
01
Money path
Draw every state a payment or loan can be in, and who can move it. Drop the states nobody uses.
02
Controls
Write the roles, dual control, and logs your compliance owner will sign. Do not invent a framework they did not ask for.
03
Ledger first
Ship posting, reversals, and a day-end file before the marketing site. Ops has to trust the number.
04
Vendors
Wire the processor and KYC tools in sandbox, then a watched production window.
05
Exception week
Run real failures: expired cards, returned payouts, a stalled webhook. Fix the queue, not the demo.
Platforms
Related platforms
Foundations we already ship that often sit in this vertical.
Stack
What we usually ship it on
- PostgreSQL
- Node.js
- Java
- Redis
- Kafka
- React
- Next.js
- AWS
FAQ
Questions, answered
Scope, hosting, and what we will not claim on this Fintech brief.
Continue
More in Regulated & High-Growth
- 01
Healthcare
Clinical records, appointments, and patient-facing tools for clinics and hospital floors.
- 02
Education
Admissions, fees, attendance, and learning tools for schools and training groups.
- 03
Real Estate
Listings, viewings, and property ops for agencies and managers who still run on sheets.
- 04
Manufacturing
Shop floor, inventory, and quality records that connect the line to the office.
Need a walkthrough for Fintech?
Book a free consultation with our solutions architects. We'll map requirements and share a clear roadmap within 48 hours.